

MCP servers
Configure a server, its credentials, and its OAuth connection.
Settings > MCP Servers is where you connect external services as tool providers for your workspace's roles.
Add a server
Click Add Tools, then:
- pick one of the Featured servers, or
- paste a remote server's URL under Add a custom server and click Continue, or
- for a local server, click Custom configuration, write its configuration as JSON and click Continue.
For a remote server that supports OAuth, choose an Authentication method:
| Method | Meaning |
|---|---|
| OAuth sign-in | Each member connects their own account before using the server. |
| Config credentials | You authenticate once, with a token or header, for the whole workspace. |
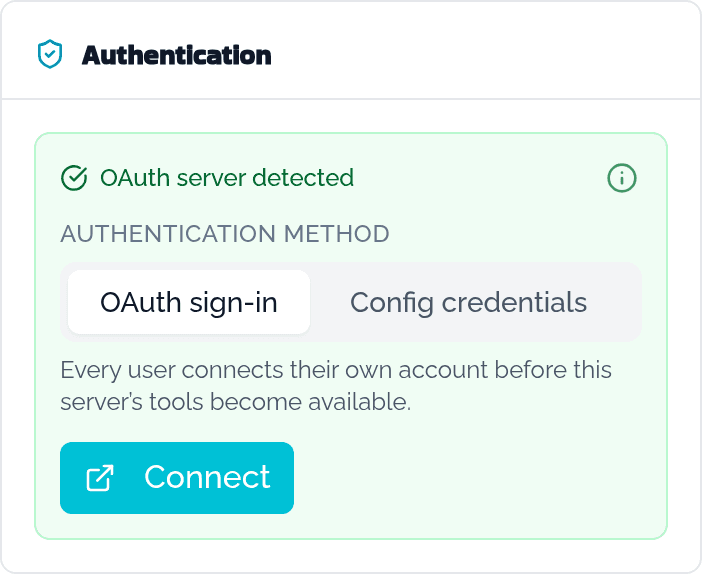
With OAuth sign-in, click Connect and sign in. A server whose sign-in lets Skilder identify itself automatically needs nothing more. Any other first asks for your OAuth app's Client ID and Client Secret.
The dialog shows its steps: Configure, Connect & test, Added. Connect & test starts once the required fields are complete. Signing in does not add the server: click Test the server to finish.
A passed test adds the server, even if the test finds no tools, and the dialog reads Test passed — your tool is added. Click Done, or Configure another server. After a failed test, the server is not added: click Try again.
Closing the dialog before a test passes discards the server, after you confirm. So does Back, once you have signed in or started a test.
Server details
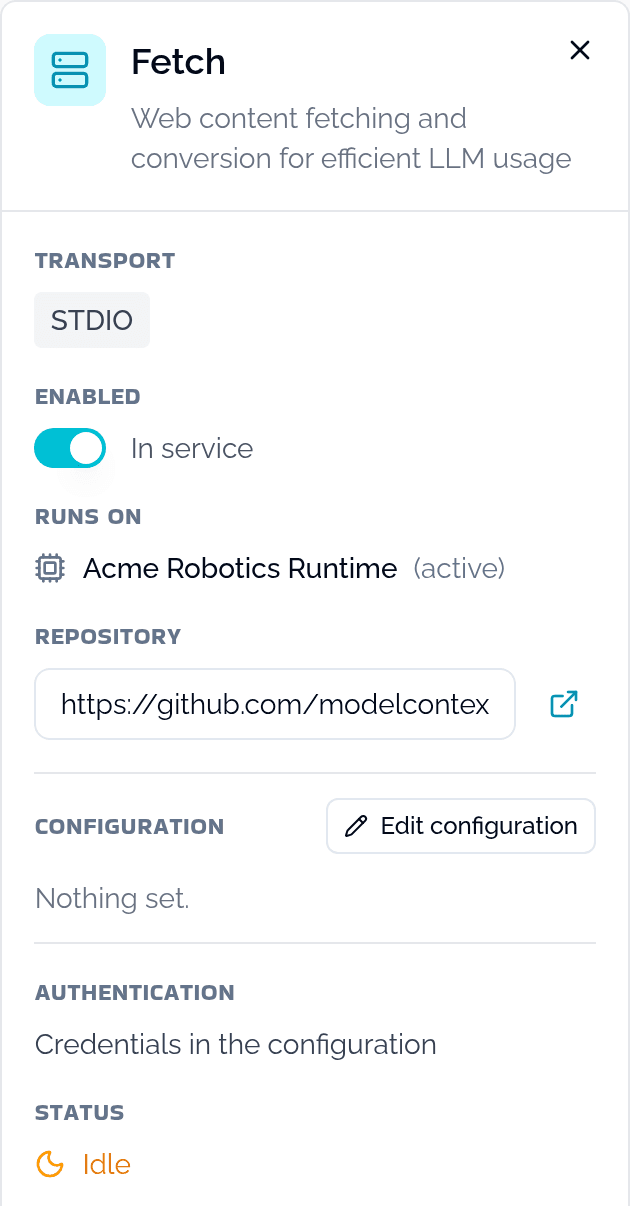
Click a server to open its detail panel:
| Field | Notes |
|---|---|
| Name, Description | Editable, saved as you leave the field. |
| Transport | Read-only, with a remote server's URL. |
| Enabled | Toggle. See below. |
| Runs on | Read-only. Assigned automatically to the workspace's runtime, not chosen per server. |
| Repository | Editable, saved as you leave the field. |
| Configuration | The arguments, environment variables or headers the server starts with. Empty ones are left out, and secrets show as dots. See Edit the configuration. |
| Authentication | How the server signs in. See Change the authentication method. |
| Status | The server's current status, such as Idle. On Error, also the last error, with a Clear error action. See Invalid config. When your own OAuth connection was revoked, its refresh failed, or a tool needs a scope the connection does not hold, it reads Needs reconnect instead, with a Reconnect button. A reconnect asks again for the scopes you granted before, plus any missing one. |
| Tools | The tools the server lists. See Refresh the tool list. |
| OAuth Integration | Admin-only. See below. |
| Your connection | Your own OAuth connection, if the server uses OAuth sign-in. See Personal integrations. |
Refresh the tool list
Skilder asks a server for its tools when it starts and when you turn it back on. A server whose list fails or comes back empty is asked again over the next few minutes, and Tools reads Discovery pending meanwhile. After that it reads Tool discovery failed with the reason, or This server offers no tools, and the server's status becomes Lists no tools instead of Error.
To ask again now, click Refresh tools beside Tools. A toast says how many tools the server listed. The button is admin-only, and stays disabled with the reason shown below it while the server cannot be asked.
A tool the server stops listing is kept, marked No longer offered, so the skills and Apps that use it stay visible. Insights lists those tools.
Edit the configuration
An edit keeps the server's tools, and so every skill that uses them. Removing the server and adding it again does not.
Under Configuration, click Edit configuration. On the Fields tab:
- Click Add argument, Add variable or Add header to add an entry, and the bin icon to remove one.
- An argument is either a --flag, with a name and a value, or a plain value.
- Click the key icon to mark a value secret. A secret is stored encrypted and hidden as you type.
- A value written as a template, such as
Bearer {token}, lists the variables it is filled from under it.
Click Save to apply your changes. An environment variable or header with a value needs a name before you can save.
To edit the configuration as JSON, open the JSON tab. Saved secrets show as ********: leave them as they are to keep them, or replace one to change it.
Each tab starts from the saved configuration, so you can switch tabs only once you have saved or cancelled your changes.
What an edit cannot change:
- the transport or a remote server's URL;
- on a STDIO server, the program that runs: its package and the version pinned in it, the arguments before the package, and environment variables that load code, such as
PATHorNODE_OPTIONS.
Add a new server for those.
Change the authentication method
Authentication lists only the methods the server can use:
| Server | Methods |
|---|---|
| Built for a provider, such as the Google or Microsoft server | That provider only. |
| Remote, whose sign-in lets Skilder identify itself automatically | OAuth sign-in, where each member connects their own account, or Credentials in the configuration, a token or header for the whole workspace. |
| Any other | Credentials in the configuration only. |
Pick one: the change is saved at once. Moving away from OAuth sign-in, or from a provider, disconnects every member connected to the server, after you confirm. A remote server's sign-in lets Skilder identify itself automatically when it accepts Skilder's published client details (a client metadata document) or lets Skilder register a client (dynamic client registration). A remote server whose sign-in supports neither is not offered OAuth sign-in here and keeps using its configuration's credentials: add it again with your own OAuth app's credentials to use OAuth sign-in.
Enable or disable a server
Toggle Enabled. A disabled server has no runtime assigned: its tools disappear from every role immediately.
Invalid config
A server whose saved configuration no longer passes validation shows Invalid config, and its status names the fields that fail. Skilder stops serving its tools, and the Enabled toggle and Clear error are not offered. Click Edit configuration: the dialog opens on the JSON tab. Fix the highlighted fields and click Save: the server comes back into service with its tools.
Skilder refuses to save an invalid configuration in the first place, and the error names the field at fault.
Install from your agent
An admin's agent can install a featured server through Skilder's manage tool, with the configuration and sign-in method offered here. If the server is already installed, the agent warns you first and only creates a second instance if you confirm. Secrets never pass through the conversation: the agent tells you what is left to fill in, and you do it on the server's page under Settings > MCP Servers, along with the OAuth client of a server that needs one.
Edit from your agent
A contributor's agent can list the workspace's servers through Skilder's manage tool, and an admin's agent can also edit one in place, with the same limits as an edit here. The agent reads each saved secret as ********. Sent back unchanged, it keeps the saved value.
Configure OAuth credentials
For a server configured with OAuth and manual client credentials (not set up automatically), click Configure credentials to open Configure OAuth:
| Field | Notes |
|---|---|
| Client ID | Prefilled with the stored value. |
| Client Secret | Write-only. Always starts blank; never returned by the API once saved. |
Auth URL, Token URL and Scopes are shown read-only for reference. Click Update Configuration to save.
A Google, Microsoft or Zoho server your agent installed has no client yet: Configure credentials sets it, with the tenant for Microsoft and the data center for Zoho. Members can connect once it is set.
Remove or duplicate a server
Delete removes the server; this cannot be undone. Copy duplicates its configuration, including its OAuth setup.
Re-registering a dynamically-registered server rotates its client credentials and disconnects every member currently connected to it. They must reconnect.
Security
- Configuration values marked secret, credential headers such as
Authorizationwhatever their flag, and OAuth client secrets and tokens are stored encrypted. - Only admins see decrypted configuration, on this page. An agent reads every secret as
********. Contributors and members, including those using a personal API key, get credential fields stripped from what they can read.